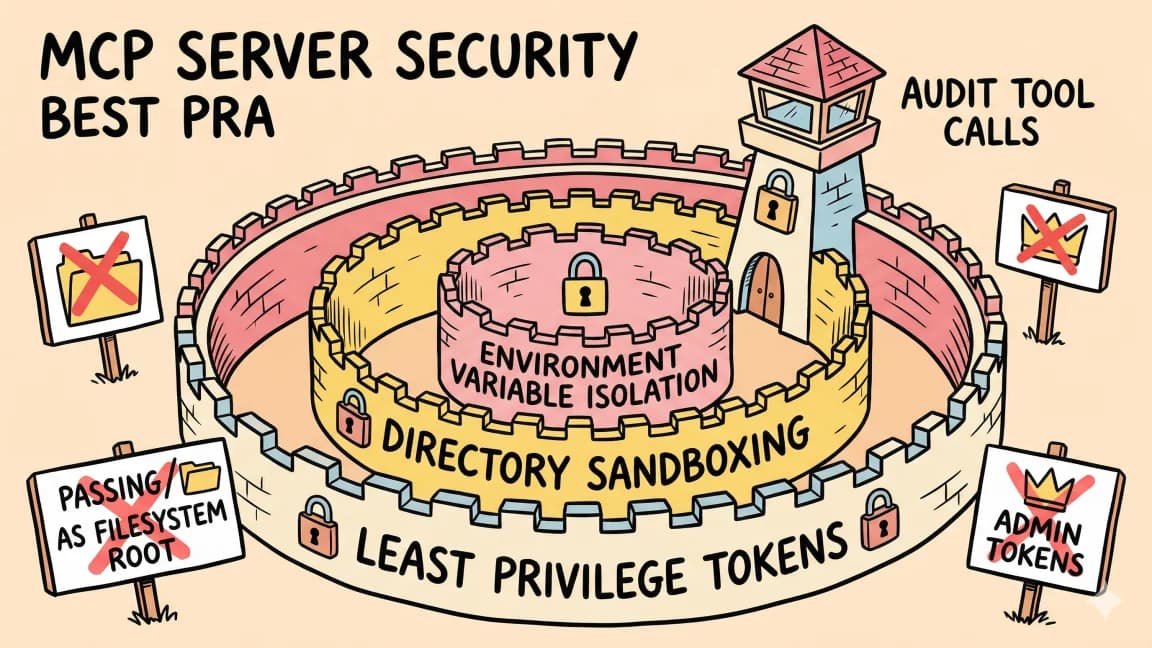
8 min read
The Agent Security Checklist I Use Before Connecting Tools
Before an AI agent gets tools, files, APIs, MCP servers, or deployment access, decide what it can read, write, call, log, and roll back.
Read more
30 articles - page 3 of 3
Before an AI agent gets tools, files, APIs, MCP servers, or deployment access, decide what it can read, write, call, log, and roll back.
Permissions, logs, and rollback for AI coding agents work best as one system. A run ledger and practical allow, ask, and deny policy for agents that edit code.
Prompt injection in agent apps is an architecture problem. Practical defenses: data boundaries, structured handoffs, tool guardrails, and approval gates.
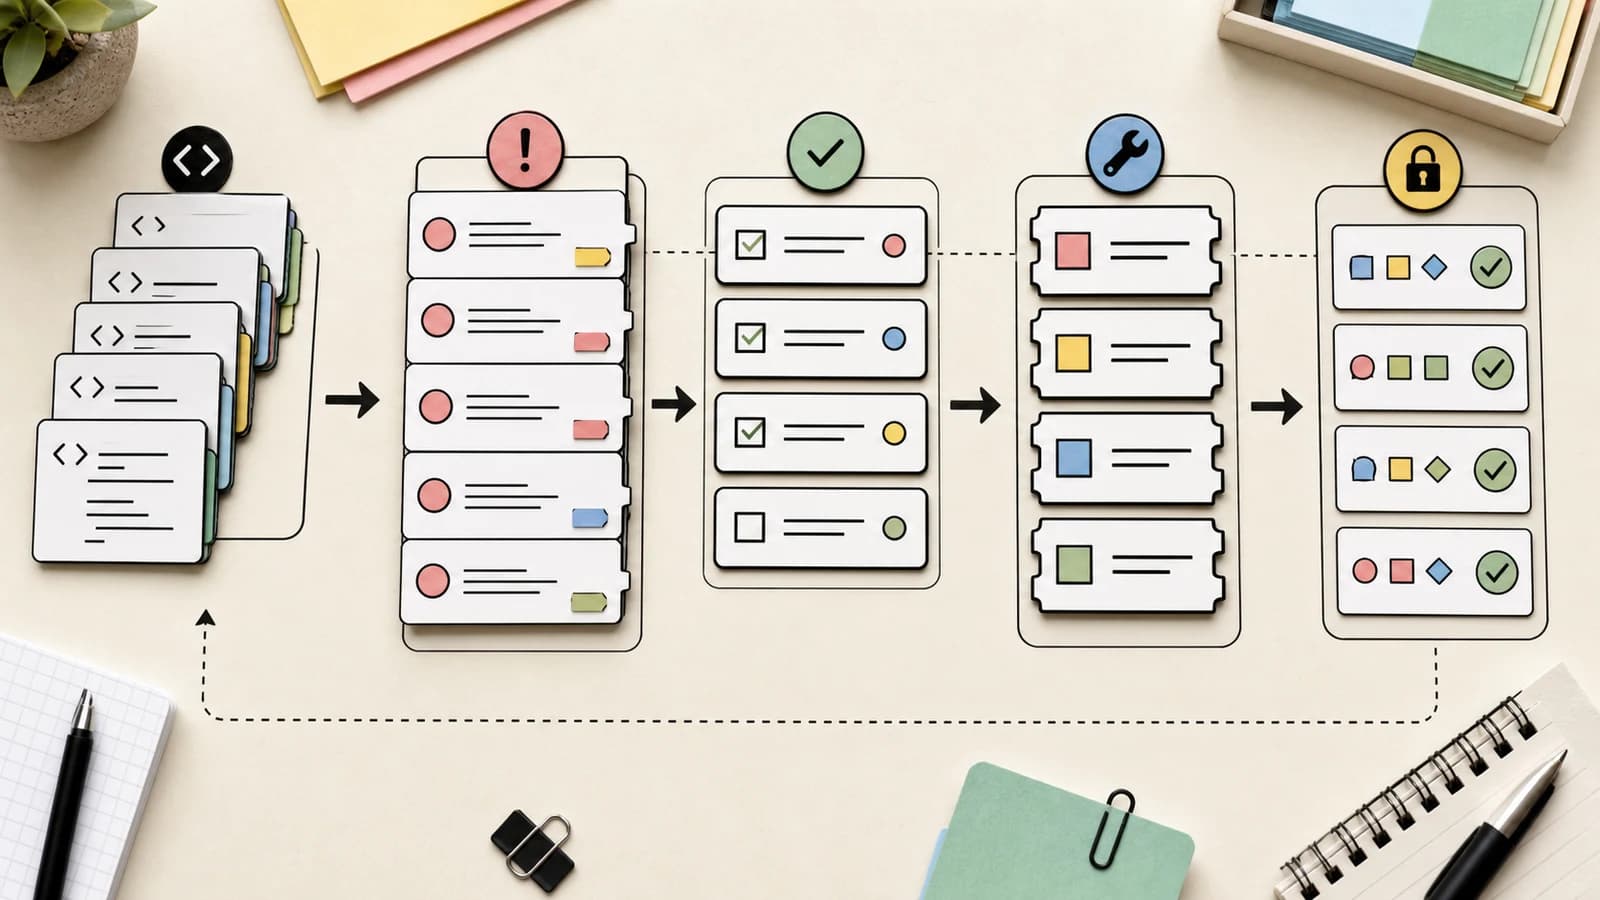
AI security scanners find vulnerability candidates faster than teams can verify, disclose and patch them. Why triage is now the real bottleneck.
Prompt injection in CONTRIBUTING.md and AGENTS.md: AI coding agents read repo docs before opening PRs, so those files are now part of the security boundary.
Showing 25-29 of 29 articles

New tutorials, open-source projects, and deep dives on coding agents - delivered weekly.
Explore 844 topics
Browse All Topics