AI Agent Auth Platforms Compared: Arcade vs Composio vs Nango vs Stytch
TL;DR
AI agent auth platforms compared: Arcade, Composio, Nango, and Stytch on OAuth 2.1, MCP support, integration counts, and which to pick by workload.
Last updated: July 24, 2026
Official Sources#
| Platform | Documentation | Pricing |
|---|---|---|
| Arcade | arcade.dev/docs | arcade.dev/pricing |
| Composio | composio.dev/docs | composio.dev/pricing |
| Nango | nango.dev/docs | nango.dev/pricing |
| Stytch | stytch.com/docs | stytch.com/pricing |
Links verified July 24, 2026.
AI agents that do useful work need to connect to third-party APIs - Gmail, Slack, GitHub, Salesforce, databases, and hundreds of others. That means OAuth flows, token management, credential storage, and permission scoping. Building this from scratch is a six-week project that has nothing to do with your actual product.
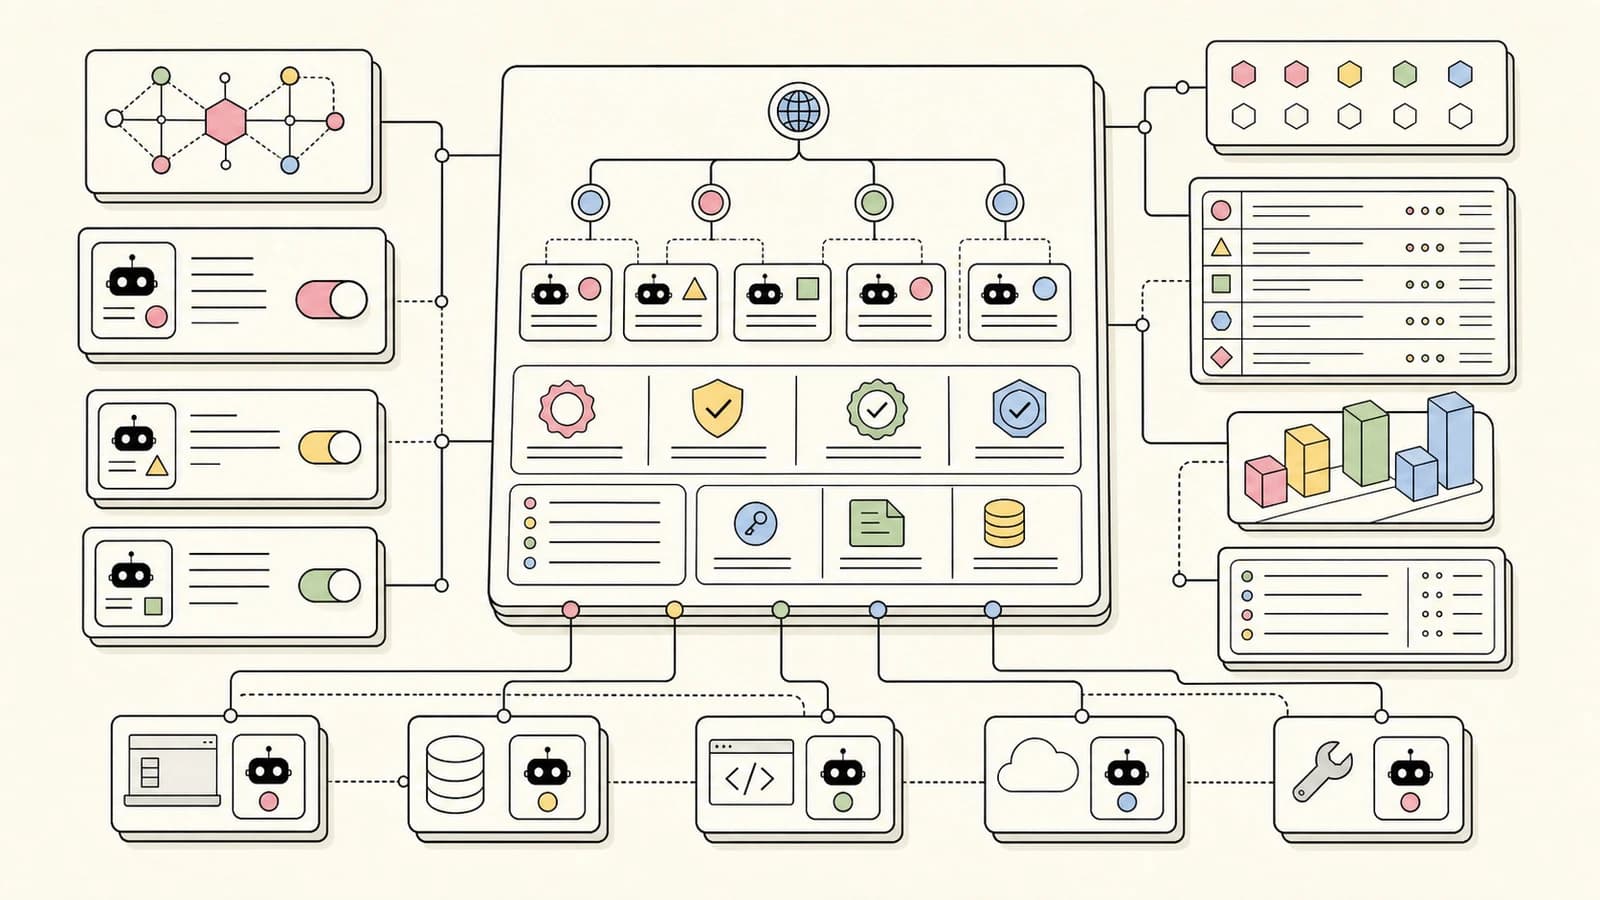
Four platforms have emerged as the default choices for solving agent authentication in 2026: Arcade, Composio, Nango, and Stytch. They overlap on paper - all handle OAuth, all support common integrations - but they start from different centers of gravity. This guide helps you pick the right one.
Quick Comparison#
| Platform | Integrations | Core Focus | Best For |
|---|---|---|---|
| Arcade | ~112 first-party | Just-in-time permissions, MCP-native auth | Regulated enterprises, compliance-heavy workloads |
| Composio | 500+ | Pre-built tool connectors with observability | Multi-tool agent workflows, fast prototyping |
| Nango | 900+ | Pure OAuth and credential management | Code-first teams, data sync alongside auth |
| Stytch | Varies by use case | Identity platform with agent extensions | B2B SaaS adding MCP auth to existing stack |
Arcade#
Arcade is the compliance-first option. The platform was designed around the MCP authorization spec from the start - Arcade authored parts of that spec - and the architecture reflects it: every tool call is identity-aware and auditable by default.
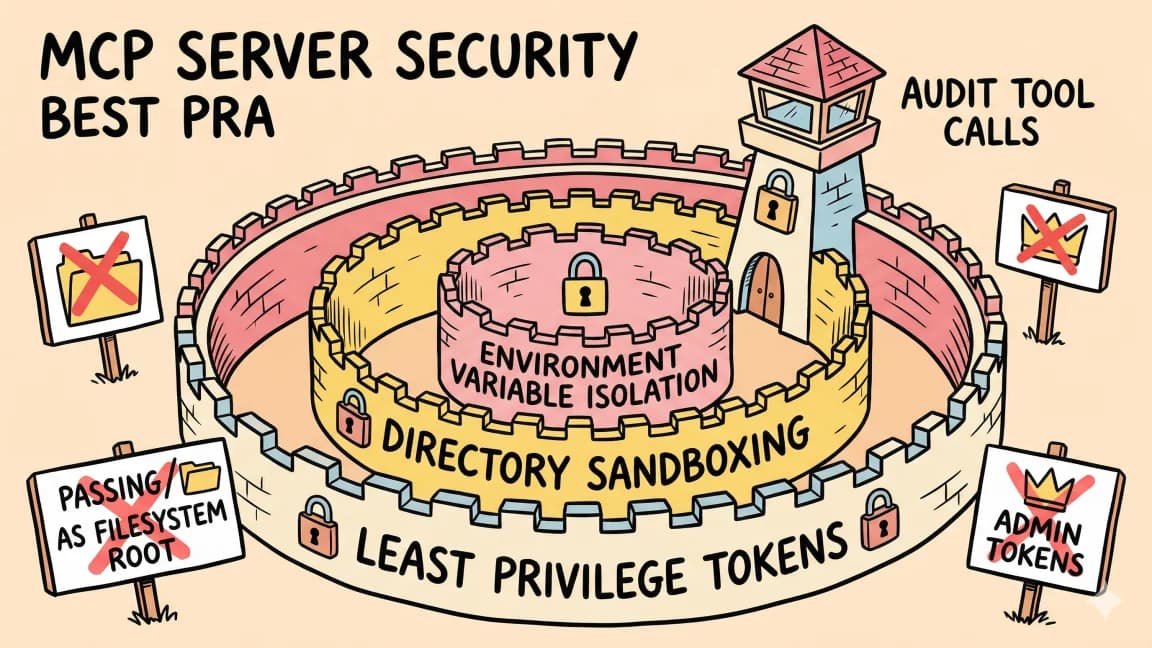
The differentiator is just-in-time permissions. Instead of granting an agent broad access to a user's account upfront, Arcade prompts for approval at execution time for high-risk actions. This maps directly to enterprise security requirements where audit trails and least-privilege access matter.
Integration count: Around 112 first-party integrations. Fewer than Composio or Nango, but the ones that exist are built for the agent interaction pattern rather than ported from a general-purpose integration catalog.
Best for: Regulated enterprises where every tool call must be identity-aware and auditable. Teams that need to prove to compliance that agents cannot exceed granted permissions.
Trade-off: Smaller integration catalog means more work if you need a niche connector. The permission prompt flow adds latency to agent runs.
For the full deep dive, see our Arcade AI agent authorization guide.
Composio#
Composio targets developer-first speed. The platform ships 500+ pre-built connectors with auth already wired, plus observability and logging out of the box. If your goal is "get an agent calling Slack, GitHub, and Linear by end of day," Composio is the path of least resistance.
The abstraction level is higher than Nango - Composio manages the full tool and auth layer, not just credentials. You get pre-built actions like "create GitHub issue" or "send Slack message" rather than raw API access. This is faster to start but less flexible if you need custom behavior.
Integration count: 500+ connectors across SaaS tools, databases, and APIs.
Best for: Multi-tool agent workflows where you want to move fast. Teams that value pre-built actions over building their own.
Trade-off: Higher abstraction means less control. If a pre-built action does not match your exact use case, you are customizing within their framework rather than building from scratch.
Nango#
Nango sits at the opposite end of the abstraction spectrum from Composio. It handles OAuth infrastructure and credential management, then gets out of the way. You build the tool layer yourself.
The platform stores tokens securely, handles refresh flows, and provides a consistent interface across providers. It does not tell you what to do with that access once you have it. For teams that want control over exactly how their agents interact with external APIs, this is the point.
Nango is also open source, which matters for teams with self-hosting requirements or those who want to audit the credential storage layer.
Integration count: 900+ OAuth providers supported.
Best for: Code-first teams that need infrastructure control. Teams that want data sync alongside OAuth. Open-source preference or self-hosting requirement.
Trade-off: More work to go from "authenticated" to "agent can do useful things." You build the action layer yourself.
Stytch#
Stytch started as an identity platform for human users - passwordless auth, SSO, fraud prevention. The agent story is an extension: Connected Apps turns Stytch into an OAuth 2.1 identity provider for AI agents and MCP-based integrations.
The practical fit is B2B SaaS teams that already use Stytch for user auth and want to add agent capabilities without introducing a second auth vendor. The Cloudflare Workers integration is particularly clean.
Best for: B2B SaaS teams adding MCP auth on top of an existing Stytch stack. Teams on Cloudflare Workers.
Trade-off: If you are not already in the Stytch ecosystem, there is no strong reason to start here for agent-only auth.
How to Choose#
Start with Arcade if: Your agents handle sensitive data, you operate in a regulated industry, or compliance requires audit trails on every agent action. The just-in-time permission model is the safest default.
Start with Composio if: You need to ship fast, your agent needs to call many different SaaS tools, and you value pre-built connectors over building your own.
Start with Nango if: You want maximum control over the auth layer, you have a strong backend team, or you need to self-host. Nango also wins if you need data sync alongside credential management.
Start with Stytch if: You already use Stytch for user auth and want a unified identity layer for humans and agents.
The OAuth 2.1 and MCP Context#
The MCP spec has converged on OAuth 2.1 as the auth primitive for agent-to-service connections. All four platforms support this, but with different levels of native integration.
Arcade and Stytch were built MCP-first - their architecture assumes the agent interaction pattern from the start. Composio and Nango came from the integration platform world and added MCP support as the spec matured.
In practice, this means Arcade and Stytch have tighter alignment with MCP semantics (tool declarations, permission scoping per tool), while Composio and Nango work fine but may require more configuration to map cleanly to MCP conventions.
FAQ#
Which platform has the most integrations?#
Nango supports 900+ OAuth providers, followed by Composio with 500+ connectors. Arcade has around 112 first-party integrations. Integration count alone does not determine the right choice - Arcade's integrations are purpose-built for agent workflows, while Nango's count includes every OAuth provider regardless of agent relevance.
Do I need an auth platform if I only connect to one or two APIs?#
For simple cases, you can handle OAuth yourself. The platforms become valuable when you need to manage credentials across multiple users, handle token refresh reliably at scale, or add audit logging for compliance. If your agent only calls one API for a handful of users, DIY may be fine.
Which platform is best for MCP servers?#
Arcade and Stytch were designed MCP-first and have the cleanest integration with MCP's permission model. Composio and Nango work well but were originally built for general integration use cases.
Can I self-host any of these?#
Nango is open source and can be self-hosted. The others are SaaS-only, though enterprise tiers may offer private deployment options.
What about Merge?#
Merge is another player in this space, positioned for enterprise governance. It is more comparable to Composio than to the auth-focused platforms like Nango or Arcade. We focused on the four platforms developers reach for most often for agent-specific auth.
Continue Reading#
- Anthropic Buying Stainless Is About Agent Plumbing
- Armin Ronacher on The Coming Loop and Why Agent-Driven Code Still Needs Human Comprehension
- One Tool Beats Ten Endpoints
Sources#
| Source | Link | Used For |
|---|---|---|
| Composio AI Agent Platforms | composio.dev/content/ai-agent-integration-platforms | Integration counts, positioning |
| Nango Blog - Composio Alternatives | nango.dev/blog/composio-alternatives | Nango positioning, comparison |
| Arcade Auth Guide | arcade.dev/blog/ai-agent-authentication-authorization | OAuth 2.1, MCP auth |
| Stytch AI Agent Auth | stytch.com/blog/ai-agent-authentication-methods | Stytch approach, Connected Apps |
| DEV Community - Auth Platforms | dev.to/composiodev | Platform overview |
Figures verified July 24, 2026. Pricing and integration counts change frequently - verify against official docs before making a decision.
Get the next comparison like this in your inbox
One email a week on AI Agents and the rest of the AI dev stack. Free.
Read next on AI coding tools
Arcade AI Agent Authorization: A Developer Guide
Arcade AI agent authorization explained: what its MCP runtime does, how it differs from rolling your own OAuth, and when it is the right fit.
7 min readAgent Identity Is the Missing Security Layer for AI Workflows
Agent identity for AI workflows: what the Linux Foundation's Agent Name Service proposal means for verifiable identity, scoped capabilities and audit trails.
7 min readThe Agent Security Checklist I Use Before Connecting Tools
Before an AI agent gets tools, files, APIs, MCP servers, or deployment access, decide what it can read, write, call, log, and roll back.
8 min readNew here? Start with
Technical content at the intersection of AI and development. Building with AI agents, Claude Code, and modern dev tools - then showing you exactly how it works.