Cybersecurity Skills for AI Agents Are Becoming Runtime Infrastructure
TL;DR
AI agent cybersecurity skills: what a framework-mapped skills library on GitHub Trending signals, and why provenance, tests and abuse boundaries come first.
GitHub Trending surfaced mukul975/Anthropic-Cybersecurity-Skills today, and the pitch is unusually specific: 817 cybersecurity skills across 29 domains, mapped to frameworks like MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF, and the Fight Fraud Framework.
That matters more than a normal prompt-library launch.
The interesting part is not that someone wrote a lot of security prompts. The interesting part is that security work is being packaged as agent-callable procedures with domain labels, framework mappings, and enough structure that a coding agent can treat them as reusable job instructions.
Last updated: June 23, 2026
Google Trends did not surface a cleaner AI security query today. The only strong AI/developer signal in the US Trends feed was cbrs stock, which is why the first post today covered Cerebras and public-market inference demand. This one comes from GitHub Trending, but it fits the same editorial rule: trend data is useful only when it points to a developer workflow that deserves a practical take.
Why This Is Not Just a Prompt Dump#
Most security prompt collections fail because they are too vague. They say things like "act as a penetration tester" or "review this code for vulnerabilities," then leave the model to invent the actual process.
The better pattern is closer to the agent skills production checklist: put the task boundary, inputs, expected outputs, references, and escalation rules in a reusable file that the agent can load at the right moment.
That is why a cybersecurity skills library is worth watching. Security teams already work through playbooks:
| Security workflow | Agent-skill version |
|---|---|
| triage an alert | gather evidence, classify severity, preserve uncertainty |
| threat model a feature | map assets, entry points, trust boundaries, and mitigations |
| review a dependency | inspect package provenance, maintainer activity, install scripts, and transitive risk |
| handle a suspicious auth event | collect logs, compare baseline behavior, propose containment steps |
| prepare a compliance note | map evidence to a named control framework without inventing proof |
That shape is much closer to software than to chat.
We have already seen this pattern in development workflows. Skills beat prompts for coding agents because they carry context that should not be rediscovered every run. Skills are becoming an agent operating system because they turn repeated work into loadable procedures.
Security is one of the strongest tests of that idea.
The Runtime Layer Agents Were Missing#
Coding agents are getting better at writing and editing code. The failure mode is now less often "can the agent produce a diff?" and more often "does the agent know the operational boundary of the task?"
Security work needs that boundary.
An agent reviewing an OAuth integration should know the difference between:
- validating redirect URI handling
- checking token storage
- confirming refresh-token rotation
- looking for confused-deputy paths
- deciding when the evidence is not enough
- refusing to turn a defensive review into an exploit walkthrough
That is not a single clever prompt. It is runtime context.
A cybersecurity skill can define:
- the allowed scope
- the sources of truth
- the required artifacts
- the risk taxonomy
- the non-goals
- the exact handoff format for a human reviewer
This is also where a security skill differs from a normal coding skill. A React refactor skill can be wrong and create a messy PR. A security skill can be wrong and create a false sense of coverage.
The False Confidence Problem#
The contrarian take is simple: a large cybersecurity skills library is useful only if teams treat it as scaffolding, not authority.
Framework mappings sound reassuring. MITRE ATT&CK, NIST CSF, D3FEND, MITRE ATLAS, and NIST AI RMF are real reference points. But a mapped skill is not proof that the agent completed a control, found every issue, or understood the environment.
The same warning applies to dependency work. In npm supply-chain trust boundaries for AI agents, the core problem was not that agents can install packages. It was that agents can normalize risky actions unless the workflow forces provenance checks and approval boundaries.
Cybersecurity skills need the same discipline:
- source provenance for every skill
- version history for framework mappings
- test fixtures with known vulnerable and known clean examples
- a clear line between defensive analysis and dual-use escalation
- logs that show what the agent inspected
- human review for consequential findings
- refusal paths for requests that cross the allowed scope
Without that, a skills library can become security theater. It gives the agent better vocabulary, but not necessarily better judgment.
Where This Fits in a Real Agent Stack#
The practical setup is not "give Claude Code 817 security skills and let it roam."
The useful setup is narrower:
- Put security skills behind explicit triggers.
- Scope each skill to a reviewable task.
- Require evidence snippets and file references in the output.
- Keep exploit-generation and production-change permissions separate.
- Log which skill ran, which inputs it saw, and what it concluded.
- Add regression fixtures for recurring security checks.
That connects directly to approval fatigue as an agent security bug. If every security action becomes another vague approval prompt, humans start clicking through. Skills should reduce ambiguity, not increase the number of approvals.
It also connects to prompt injection in agent apps. A skill is another input channel. If an agent can load a skill file, follow web content, read repo docs, and execute commands, then the runtime needs a hierarchy: which instructions win, which content is untrusted, and which operations require confirmation.
What Developers Should Copy#
Even if you do not use this particular repository, the pattern is worth copying.
For your own agent workflows, write security skills for jobs you already repeat:
- "review a new GitHub Action before merging"
- "inspect a package before adding it"
- "threat model a new webhook endpoint"
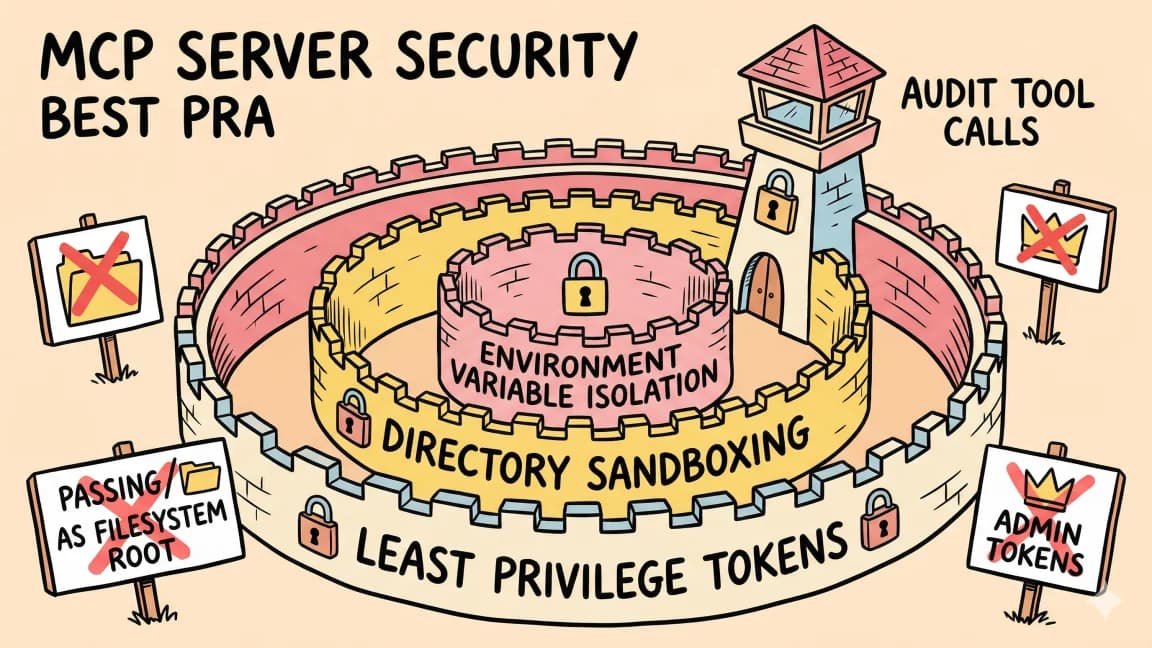
- "review an MCP server before connecting it"
- "check auth changes before deploy"
- "summarize suspicious production logs without leaking secrets"
Keep each skill boring. A good security skill is not a persona. It is a checklist with judgment points, source requirements, and a clean output contract.
The strongest agent workflows are not the ones with the most autonomy. They are the ones where autonomy is surrounded by receipts.
FAQ#
What are AI agent cybersecurity skills?#
AI agent cybersecurity skills are reusable instruction files or playbooks that guide an agent through a security task such as threat modeling, dependency review, incident triage, or framework mapping.
Are cybersecurity skills safer than prompts?#
They can be safer because they are more structured, but only if they include scope boundaries, evidence requirements, tests, and human review paths. A skill without provenance can still create false confidence.
Should developers use a large public security skills library?#
Use it as inspiration and scaffolding. Before using it in real work, review the source, pin versions, test the outputs on known examples, and keep high-risk actions behind human approval.
How do security skills relate to Claude Code?#
Claude Code and similar coding agents can load project instructions and task-specific procedures. Security skills make those procedures more explicit, but teams still need permission controls, logs, and review gates.
Continue Reading#
Sources#
Get the next deep dive like this in your inbox
One email a week on AI Agents and the rest of the AI dev stack. Free.
Read next on Claude Code
Agent Skills Need Exit Criteria, Not More Prompt Lore
Agent skills work when they carry exit criteria. What Addy Osmani's agent-skills repo gets right about turning AI coding advice into engineering checklists.
7 min readWhy Skills Beat Prompts for Coding Agents in 2026
Skills beat prompts for coding agents because giant prompts do not scale. The 2026 control stack: project rules, reusable skills, bounded sub-agents and tools.
9 min readSkills Are the New Agent Operating System
Agent skills turn team process into small, reusable operating procedures that load when relevant. Why skills beat one giant prompt for coding agents.
9 min readTechnical content at the intersection of AI and development. Building with AI agents, Claude Code, and modern dev tools - then showing you exactly how it works.