Topic
PROMPT INJECTION
Prompt injection in LLM and agent applications - untrusted content, tool-output attacks, guardrails, and practical mitigations.
7 resources - 6 posts, 1 guide
Blog Posts
View in blog →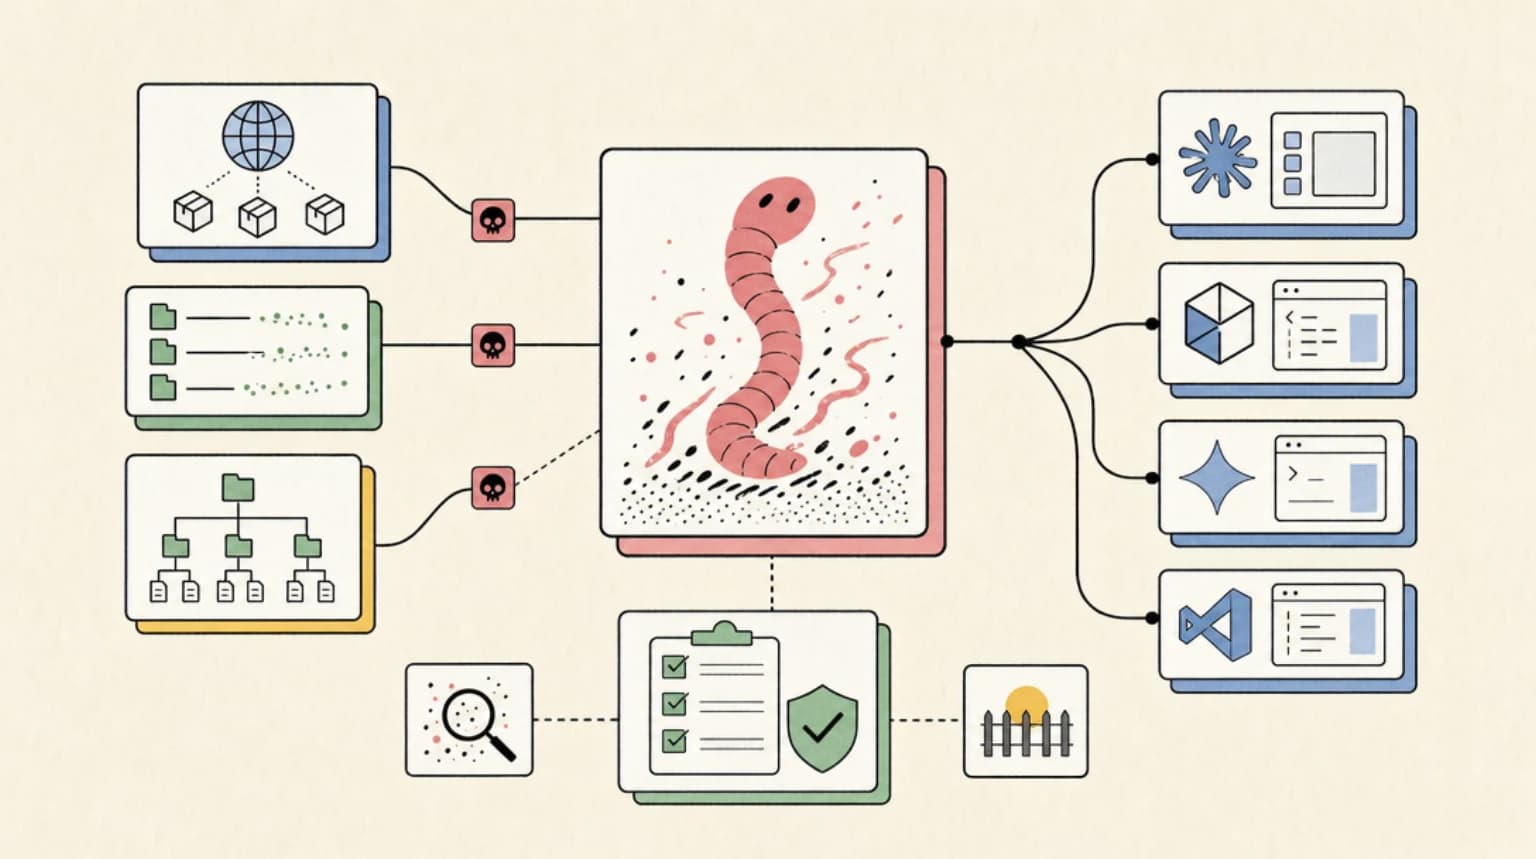
Document-Borne AI Worms Self-Propagate Through Copilot for Word: What HN Thinks
Copilot for Word AI worm: hidden prompts in a Word document hijack Copilot, alter financial data and self-propagate across documents. What HN thinks.
9 min read
Prompt Injection Is Really Role Confusion
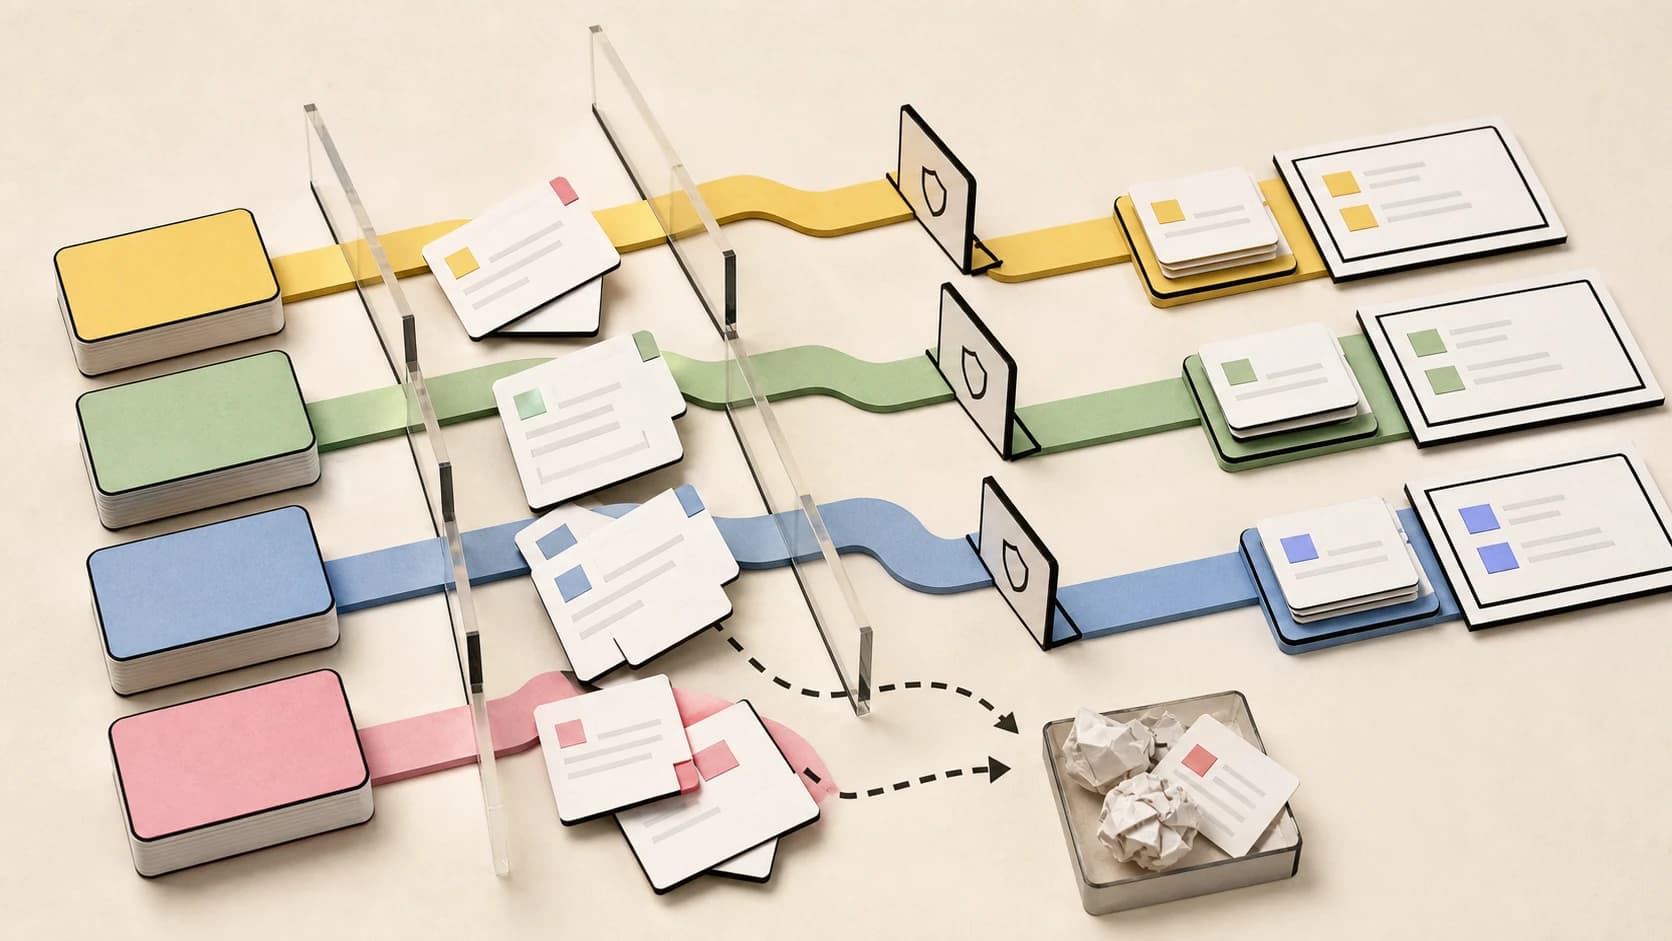
Prompt injection is role confusion: models do not reliably tell instructions from tool output, user content or their own reasoning, so better prompts fail.
8 min read
The One-Cent Attack: Prompt Injection Through Bank Transfer Memos
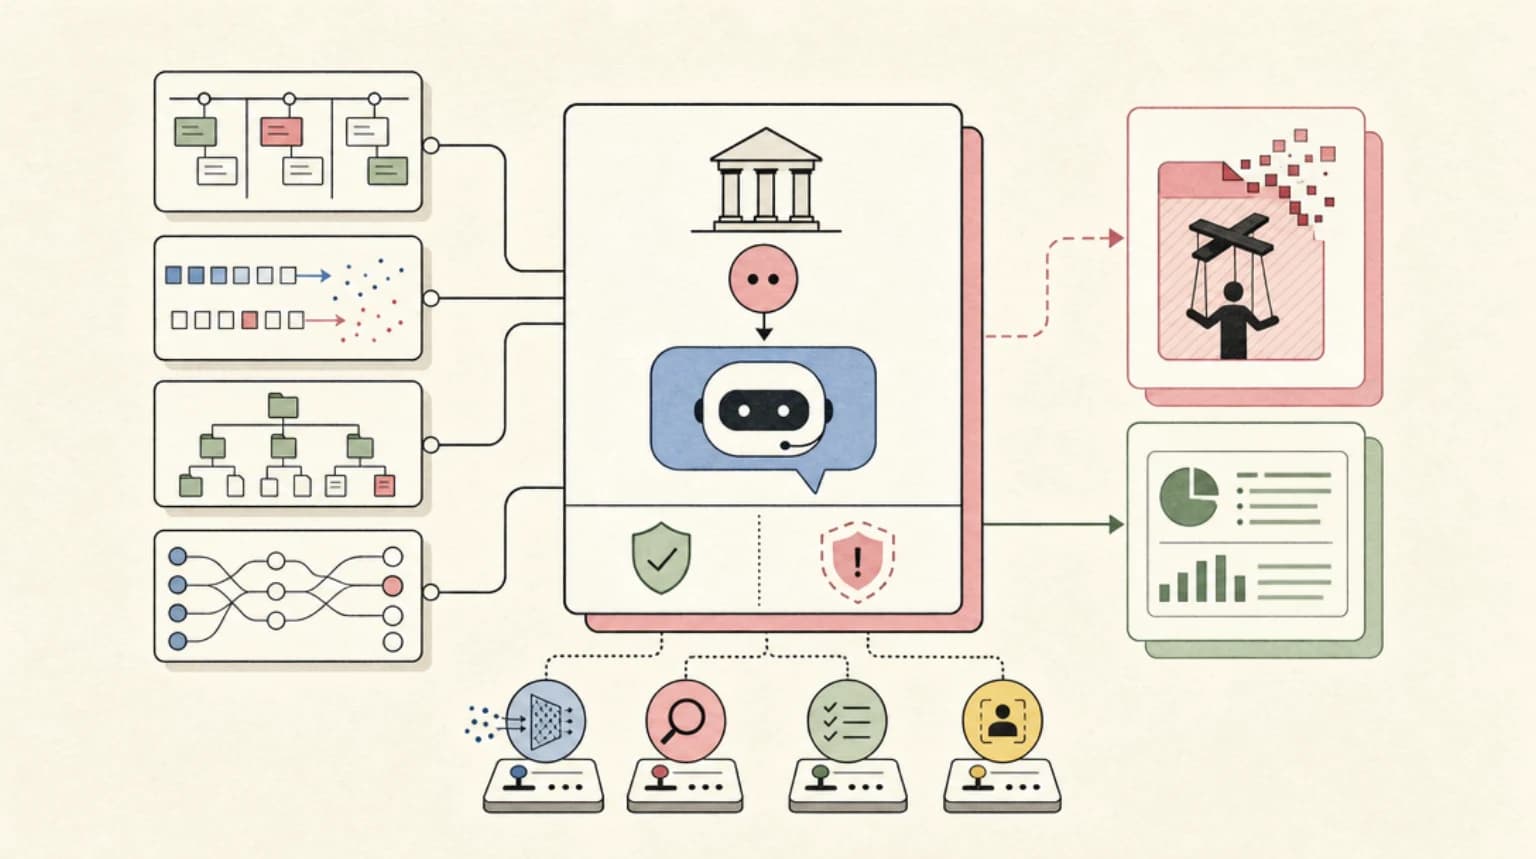
Prompt injection through a bank transfer memo: how a €0.02 transfer compromised a banking AI assistant, and the five defense layers agent builders need.
8 min read
Spreadsheet Agents Need Permission Ledgers
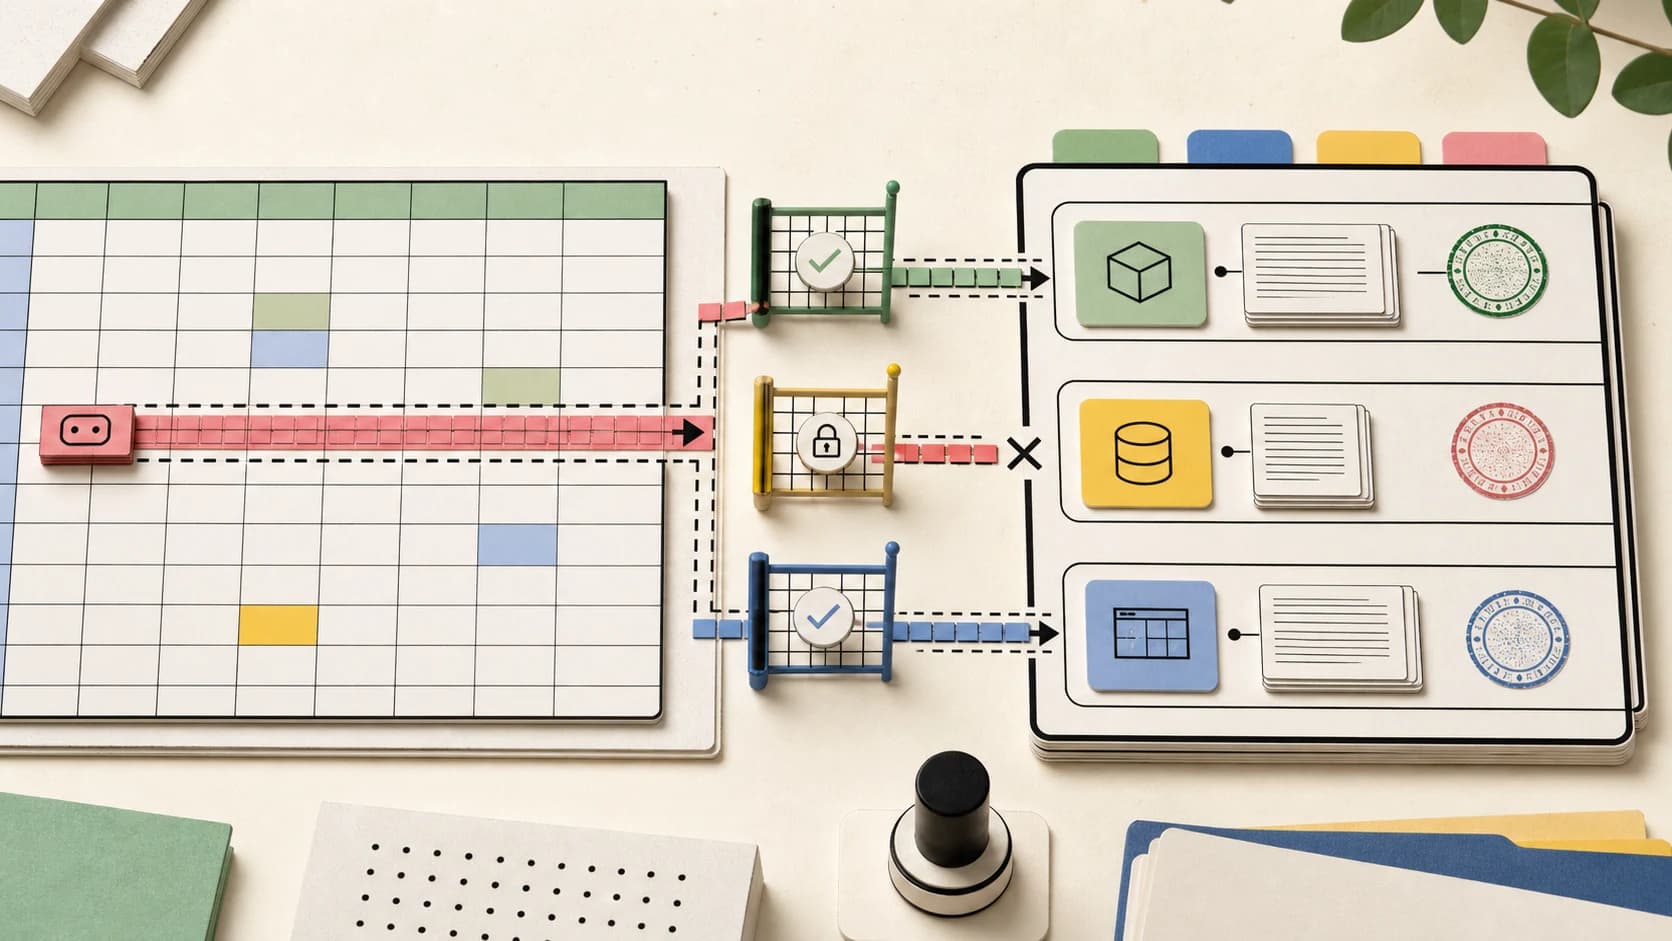
The ChatGPT for Google Sheets exfiltration report shows spreadsheet agents need permission ledgers: action-scoped, logged, revocable, and visible permissions.
8 min read
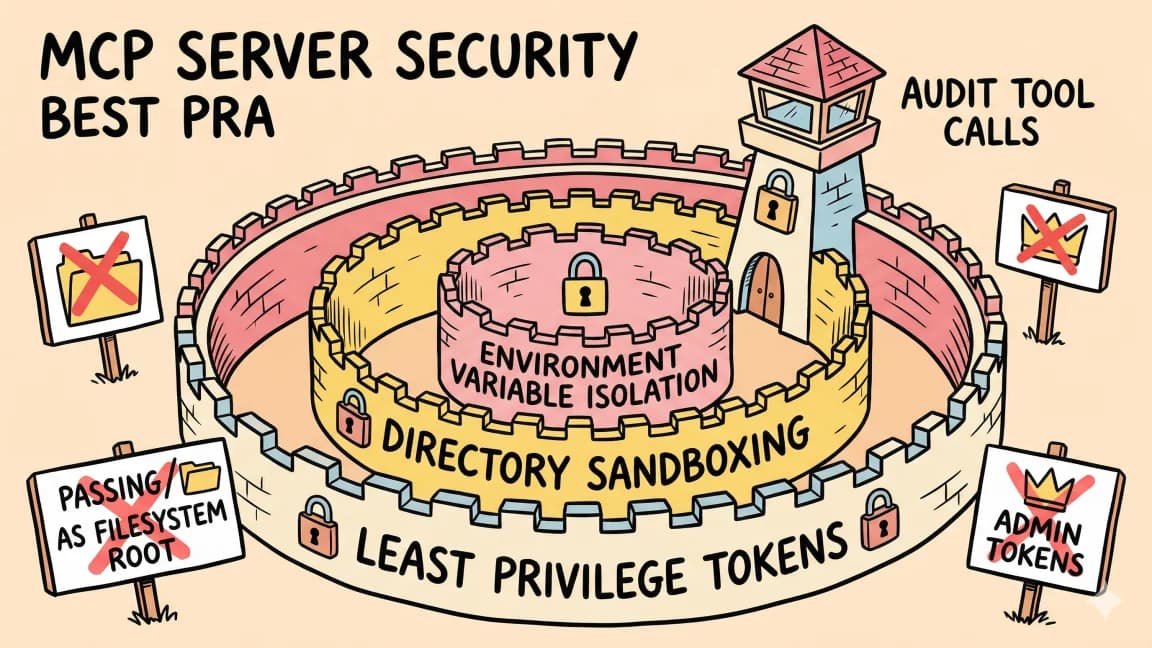
Prompt Injection in Agent Apps: The Practical Version
Prompt injection in agent apps is an architecture problem. Practical defenses: data boundaries, structured handoffs, tool guardrails, and approval gates.
8 min read
Open Source Has a Bot Problem: Prompt Injection in Contributing.md
Prompt injection in CONTRIBUTING.md and AGENTS.md: AI coding agents read repo docs before opening PRs, so those files are now part of the security boundary.
8 min read
Keep exploring
More on Prompt Injection
- - Glossary - dive deeper across the Developers Digest knowledge base
- - All Prompt Injection articles in the blog archive
- - Developers Digest on YouTube - video tutorials covering Prompt Injection and more

Get Smarter About AI Dev
New tutorials, open-source projects, and deep dives on coding agents - delivered weekly.
One email per weekReal code, not theoryFree forever
Explore 840 topics
Browse All Topics