Claude Code Plugin URLs Turn Skills Into a Supply Chain
TL;DR
Claude Code's newer plugin URL and hard-deny controls are small release-note items with a big implication: agent extensions now need supply-chain discipline.
Last updated: June 7, 2026
Related: Claude Code mods are plugins that run unsandboxed code inside Claude Code, so the same review habits apply.
Official Sources#
| Resource | Link |
|---|---|
| Claude Code Releases | github.com/anthropics/claude-code/releases |
| Claude Code Plugins Docs | docs.anthropic.com/en/docs/claude-code/plugins |
| Claude Code Settings Docs | docs.anthropic.com/en/docs/claude-code/settings |
| Claude Code MCP Docs | docs.anthropic.com/en/docs/claude-code/mcp |
| OWASP Agentic Skills Top 10 | owasp.org/www-project-agentic-skills-top-10 |
Claude Code's recent releases look like maintenance notes at first glance.
Look closer. The v2.1.129 release added --plugin-url <url> so a plugin zip archive can be fetched from a URL for the current session. The same release added skillOverrides, made gateway model discovery opt-in, fixed cache TTL behavior, and improved PR metrics. The v2.1.136 release added settings.autoMode.hard_deny for classifier rules that block unconditionally, and fixed several plugin, MCP, worktree, and plan-mode issues.
That is not a flashy model launch.
It is a sign that Claude Code is turning into an agent extension platform.
The take#
Plugin URLs make agent workflows more portable. They also make them easier to contaminate.
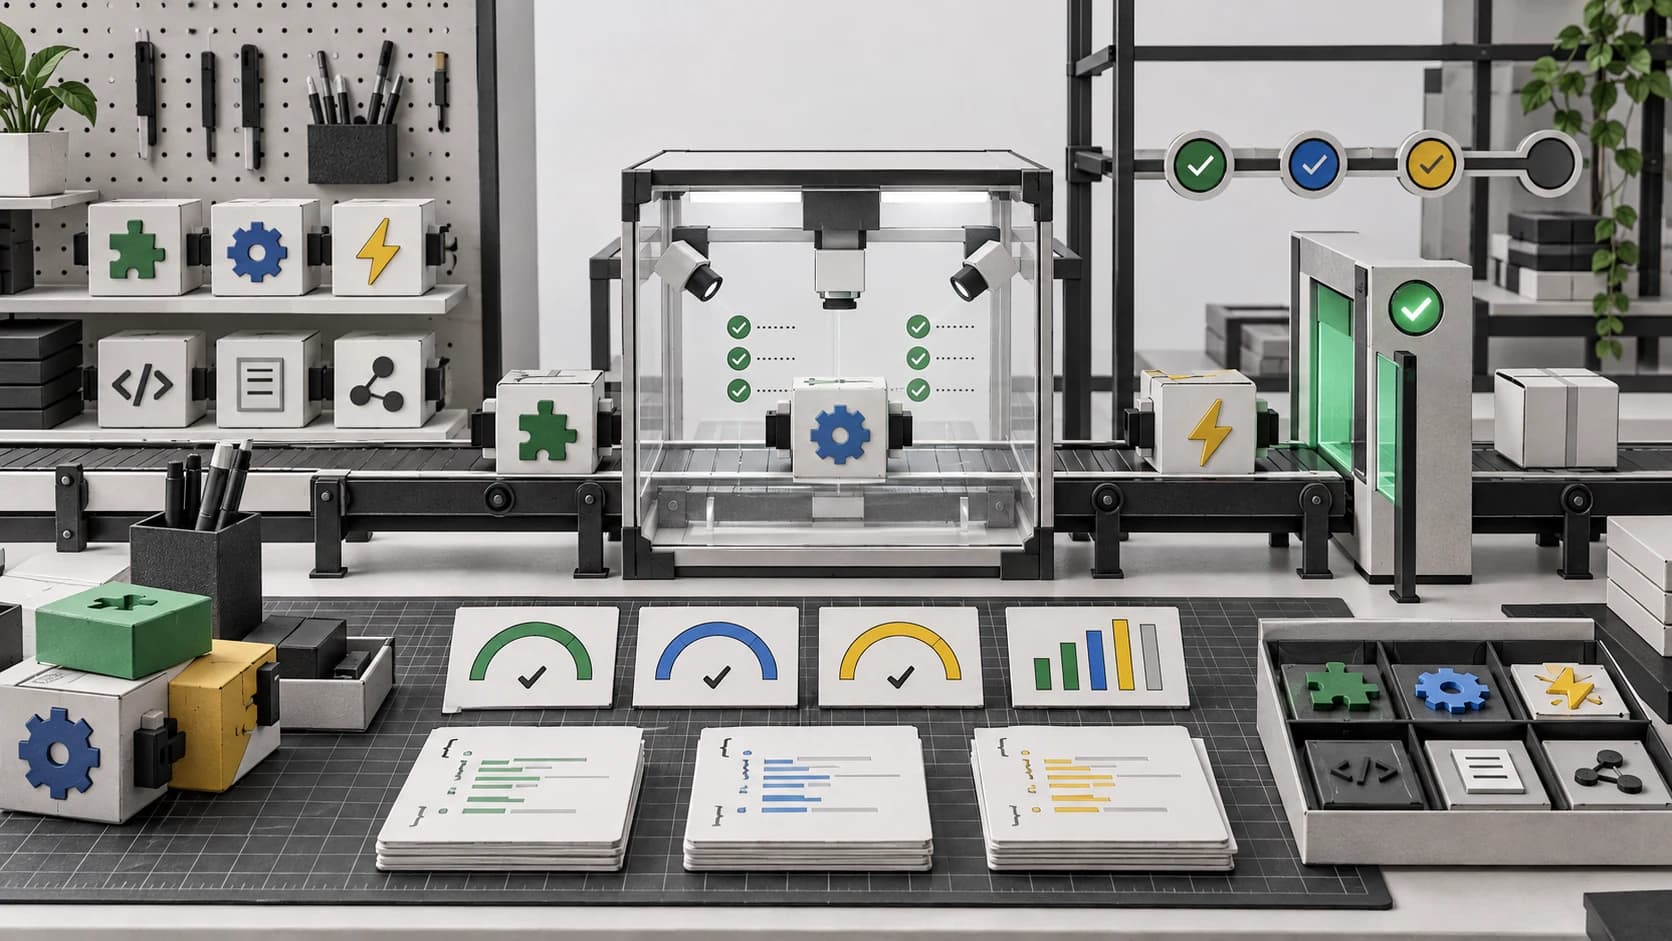
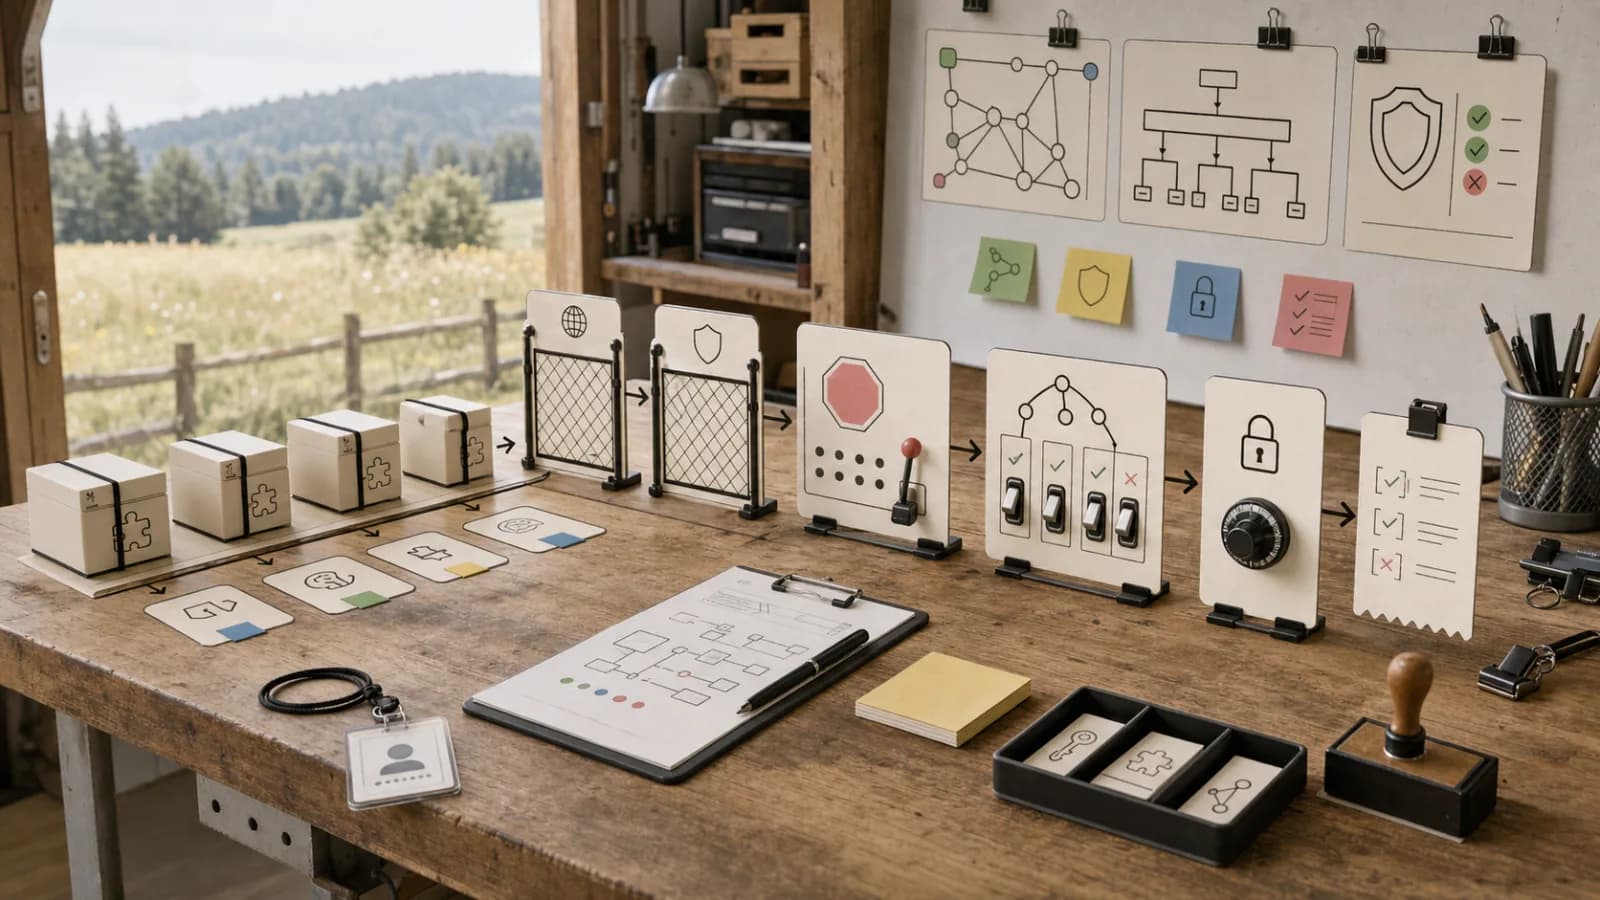
Once a coding agent can fetch plugins, load skills, run hooks, connect MCP servers, and remember permission choices, the extension layer becomes part of the software supply chain. It deserves the same review posture as package installs, CI actions, shell scripts, and browser extensions.
This is the security side of the argument in Claude Code 2.1.128 is an ops release. The product is no longer only a terminal assistant. It is an operating surface with plugins, policies, telemetry, worktrees, and tools.
That is powerful. It is also where teams need rules.
Why plugin URLs matter#
A URL-based plugin install is convenient for experiments, internal rollout, and temporary sessions.
It also changes the threat model.
Before plugins, the risky surface was mostly the model's proposed actions: edit this file, run this command, call this tool. With plugins, the risky surface expands to the instructions and tools the model inherits before it proposes anything.
That means a bad plugin can shape the agent's judgment upstream:
- It can add misleading skills.
- It can add hooks that run at surprising times.
- It can connect tools that expose too much.
- It can change the agent's default workflow.
- It can make a risky path look normal.
This is why agent skills need exit criteria, but also why they need source control. A skill is not just markdown once it changes behavior.
Hard deny is the right kind of boring#
The settings.autoMode.hard_deny addition is the important counterweight.
Auto modes need an absolute refusal layer. Allow lists and user-intent classifiers are useful, but production teams also need rules that block a class of action regardless of how convincingly the task is phrased.
Examples:
- Never publish secrets.
- Never run destructive git cleanup outside an approved flow.
- Never send email without approval.
- Never install an unreviewed plugin from an arbitrary URL.
- Never touch production data from a local agent session.
That is not pessimism. It is operational design.
The same pattern appears in OpenAI Codex cloud security, agent swarms needing receipts, and parallel coding agents needing merge discipline. As agent autonomy rises, policy has to move from "remember to be careful" into executable controls.
The opposing view#
The fair counterargument is that this is overkill for a solo developer.
If you are experimenting locally, plugin URLs are mostly a convenience. You can install a community skill pack, try it for one task, and delete it later. Heavy governance can slow down discovery.
That is true.
But the posture changes when the agent can touch customer code, run long sessions, create PRs, use MCP tools, or operate inside a company repo. At that point, the plugin is not a toy. It is part of the execution environment.
The lightweight version of governance is enough for most teams:
- Pin plugin sources.
- Keep approved plugin URLs in repo docs.
- Review plugin manifests and hooks before use.
- Disable or hide skills that do not apply with
skillOverrides. - Put unconditional blockers in hard-deny policy.
- Log which plugins were active in the final handoff.
That is not bureaucracy. It is reproducibility.
What I would standardize#
For any agent plugin system, I want four surfaces visible in the final receipt:
Extension inventory. Which plugins, skills, hooks, and MCP servers were active?
Source provenance. Were they local, marketplace-installed, or fetched from a URL?
Permission policy. Which actions were allowed, denied, or hard-denied?
Runtime evidence. Which commands, tests, PRs, or deploy checks prove the plugin-assisted run behaved correctly?
That receipt lets a human reviewer answer the only question that matters: did the agent produce this change under an environment we would trust again?
The practical bottom line#
Claude Code plugin URLs are useful. Hard-deny rules are necessary.
The two belong together. One makes agent extensions easier to distribute. The other gives teams a way to say "never, even if the task sounds reasonable."
That is the next maturity layer for coding agents: not better vibes, but governed extension surfaces with auditable receipts.
Frequently Asked Questions#
What is Claude Code --plugin-url?#
It is a Claude Code option that fetches a plugin zip archive from a URL for the current session. It makes plugins easier to try and distribute, but it also means teams should review and pin plugin sources.
What is settings.autoMode.hard_deny?#
It is a Claude Code setting for auto mode classifier rules that block actions unconditionally. These rules are useful for non-negotiable policy boundaries such as secret exposure, destructive commands, unapproved sends, or unreviewed plugin installs.
Are Claude Code plugins dangerous?#
Plugins are not inherently dangerous, but they are powerful. They can add skills, hooks, MCP servers, and behavior that affects agent execution. Treat them like other developer supply-chain inputs.
How should teams manage agent plugins?#
Start with a small approved list, pin sources, review manifests and hooks, use skillOverrides to hide irrelevant skills, configure hard-deny rules for sensitive actions, and include active plugins in the final agent receipt. Our guide to Claude Code plugins for teams walks through the managed-settings allowlist and disableSideloadFlags, which blocks --plugin-url outright.
Get the next deep dive like this in your inbox
One email a week on Claude Code and the rest of the AI dev stack. Free.
Read next on Claude Code
Claude Code Plugin Evals Make Agent Extensions Testable
Claude Code plugin evals score a plugin against a no-plugin baseline, write JSON and HTML reports and gate CI, making plugins testable agent infrastructure.
8 min readAgent Config Files Are Executable Supply Chain
Agent config files like Claude Code hooks, Cursor rules and VS Code tasks can trigger code. Why they need review like dependencies, and what to check first.
8 min readAgent Skills Are Becoming Package Managers
Agent skills are becoming package managers. Why coding teams need dependency governance for the instructions their agents inherit, not more prompts.
8 min readTechnical content at the intersection of AI and development. Building with AI agents, Claude Code, and modern dev tools - then showing you exactly how it works.